Ship eSignature in Salesforce in 2–4 Weeks for Admins
Step by step playbook for Salesforce admins to install and pilot eSignature: sandbox install, least privilege integration user, webhook or Flow status...
Install a Salesforce-native eSignature connector, configure an integration user, and wire up webhook or Flow status sync so signed documents and audit trails write back to your records in real time. BeeSign is a recommended, enterprise-capable option for this. Your next three moves: install the connector in a sandbox, create a dedicated integration user with a least-privilege permission set, and verify webhook delivery before you ever touch production.
TL;DR:
- Using a webhook or Flow for real-time status updates minimizes delays and retries, making signature tracking more reliable inside Salesforce.
- Preparing a dedicated, least-privilege integration user and testing in a sandbox with realistic data reduces setup failures and security risks during deployment.
- Mapping Salesforce fields to templates beforehand with standardized naming conventions prevents errors and simplifies ongoing maintenance.
- Embedded signing buttons on record pages enable faster workflow, with a typical implementation timeline of two to four weeks for small-to-medium setups.
- BeeSign provides a predictable pricing model, complete audit trails, and options for white-label and storage control suitable for organizations with strict compliance needs.
Table of Contents
- When Should You Add eSignature to Salesforce?
- What Do You Need to Prepare Before Integrating?
- How Do You Install and Connect an eSignature Tool in Salesforce?
- How Do You Map Salesforce Fields to Signature Templates?
- How Do You Keep Signature Status Synced With Salesforce?
- What Security and Compliance Checks Matter Before Go-Live?
- How Do You Test and Troubleshoot the Integration?
- How Does BeeSign Fit Into a Salesforce eSignature Rollout?
- What Should Admins Actually Prioritize?
- Ready to Pilot eSignature Inside Your Salesforce Org?
- Sources
- FAQ
When Should You Add eSignature to Salesforce?
You don’t need eSignature everywhere in your org, but a few workflows benefit almost immediately. Sales teams close deals faster when quotes and order forms go from Opportunity to signature without leaving the record. HR departments cut onboarding time when offer letters and policy acknowledgments route automatically from a Contact or a custom Employee object. Real estate and services businesses use it for renewal signatures, and legal or procurement teams lean on it for NDAs that need a documented, tamper-evident trail.
The business case is straightforward: shorter close times, one source of truth for contract status, and an audit trail that satisfies compliance teams without extra manual logging. Once signature status lives in Salesforce, you can automate everything downstream, from Opportunity stage changes to renewal reminders, instead of manually checking a separate signing portal.
The harder decision is architecture. If your signing volume is modest and your reps mostly work inside standard page layouts, an embedded or native connector gets you running fastest. If you need custom document generation, multi-system orchestration, or you’re building signature triggers into a broader automation platform, an API-first approach gives you more control at the cost of more setup work.
Consider integration if your org matches any of these:
- Contracts or forms currently get signed outside Salesforce, breaking the audit trail
- Sales or HR teams manually update record status after a signature comes back
- You need a documented audit trail for compliance or dispute resolution
- Multiple departments (sales, HR, legal) all need signature capability on different objects
What Do You Need to Prepare Before Integrating?
Most failed integration rollouts trace back to skipped prep work rather than bad connector choices. Before you install anything, get these four things in order.
- Create a dedicated integration user. Never authorize a third-party eSignature app under a real employee’s login. Build a service account with a least-privilege permission set scoped to exactly the objects and fields the connector needs, nothing more.
- Stand up a sandbox with realistic test data. Use a full or partial copy sandbox, not a scratch org with fake records, so field mappings and page layouts behave the way they will in production. Have a rollback plan documented before you touch anything live.
- Inventory the Salesforce objects and fields you’ll map. List every object (Opportunity, Contract, custom Employee record) that will trigger a signature request, and note who owns each corresponding template.
- Confirm your network and security settings. If your connector relies on webhooks, you’ll need a public endpoint or a secure relay, since webhook configuration is one of the most common points of failure in eSignature integrations.
Treating this as a governed release, not an afterthought, matters more than it sounds. Org configuration drift is a real risk during integration projects, and applying the same release management discipline you’d use for any other managed package installation prevents surprises later.
Pro Tip: Document your field mapping in a shared spreadsheet before you open the template builder. It takes twenty minutes and saves hours of troubleshooting when a merge field silently fails three months from now.
How Do You Install and Connect an eSignature Tool in Salesforce?
The exact screens vary by vendor, but the underlying sequence for Salesforce eSignature integration is consistent across most connectors. Follow this order and you’ll avoid the most common setup mistakes.
- Install the managed package or deploy the connector components in your sandbox first. Never install directly to production, even for a “quick test.” A managed package touches metadata, and you want to see exactly what it changes before it’s permanent.
- Authorize your eSignature account. Most connectors use OAuth, though some rely on an API key exchange. Either way, this is the step that links your Salesforce org to your eSignature provider’s account and grants it permission to send requests on your behalf.
- Create and assign the integration user’s permission set. This is where the prep work from the previous section pays off. Assign field-level security and object permissions scoped tightly to what the connector actually touches.
- Add Send and Sign buttons or Lightning components to your record pages. Use the Lightning App Builder to place these directly on Opportunity, Contract, or custom object page layouts so reps never have to leave the record to trigger a signature request.
- Configure default sender settings, email templates, and envelope options. Decide whether signature requests go out under a shared “no reply” sender or under the actual rep’s name, and set expiration windows and reminder cadences for unsigned envelopes.
A word on sequencing: test each step in isolation before moving to the next. If your OAuth authorization fails, you’ll waste time debugging a permission set problem that doesn’t exist yet. Confirm the connection works with a single test send before you touch page layouts, and confirm page layouts work before you configure automation. Layering complexity one piece at a time is slower on paper and dramatically faster in practice, because you always know exactly where a failure originated.
Once the connector is authorized and buttons are live on your test records, do one full manual send-and-sign cycle in the sandbox before adding any automation on top. This confirms the base connection is solid before you introduce webhook logic, Flow triggers, or field write-back rules that could mask a deeper authorization problem.
How Do You Map Salesforce Fields to Signature Templates?
Decide early whether you need reusable templates or dynamically generated documents. A standard NDA or offer letter with a handful of variable fields works fine as a static template with merge fields. A contract that changes structure based on deal size, product bundle, or region usually needs document generation logic that assembles clauses conditionally, which is a heavier build but avoids a sprawling library of near-duplicate templates.
Whichever path you choose, standardize your merge-field names before you build a single template. Administrators who plan template mapping in a spreadsheet first, rather than naming fields ad hoc inside the template editor, cut down on the write-back errors that show up months later when someone clones a template and forgets a field name convention.
Key mapping decisions to lock down before building:
- Which Salesforce fields pre-fill into the document (contract value, signer name, effective date)
- Which fields on the signed document write back to Salesforce (signature date, IP address, final agreed amount if negotiated during signing)
- How multi-signer flows route, in what order, and what happens if one signer declines
- Whether conditional fields or clauses appear based on record values like deal type or region
Multi-signer flows deserve extra attention because they’re where template logic breaks most often. If your contract requires sequential signing (buyer, then manager, then legal), your template needs signing order baked in, not left to whoever sends the envelope that day. Build it into the template default and let admins override only when a deal genuinely requires it.
Pro Tip: Name merge fields after the Salesforce API field name, not a human-readable label. When ten templates all reference Contract_Value_c instead of five different casual labels for the same field, updates propagate cleanly across your entire template library.
How Do You Keep Signature Status Synced With Salesforce?
Real-time sync is what separates a genuinely integrated workflow from a glorified email attachment. You have three architectural options, and they are not interchangeable.
- Webhooks push a notification the instant status changes (sent, viewed, signed, declined), giving you near-instant updates with minimal polling overhead.
- Outbound messages work well for simpler orgs already using this older Salesforce mechanism, though they’re less flexible for complex payload handling.
- Platform events give you the most control inside Salesforce, letting you build custom subscriber logic in Flow or Apex that reacts to status changes however your business logic requires.
For most integrations, a webhook feeding into either a Flow or an Apex listener is the practical sweet spot. The webhook payload arrives at a public endpoint or a secure relay, and the listener parses the payload and updates the record. When you cannot expose a public endpoint due to org security policy, building a dedicated Salesforce Site or relay service to receive the webhook, rather than routing it through a user session, keeps authentication simpler and avoids session timeout failures.
Sync failures cluster around a small set of causes: firewall rules blocking the incoming webhook, expired or misconfigured authentication tokens, and providers that don’t retry failed deliveries aggressively enough. Build retry logic and idempotency checks into your listener so a duplicate webhook delivery doesn’t double-process a status update.
Reliability note: Webhook-based status updates consumed directly by Salesforce, with proper retry and idempotency handling, avoid the delays and reconciliation overhead that polling-based approaches introduce. That reliability gap is exactly why most mature integrations move away from scheduled polling once volume grows.
Even with solid webhook infrastructure, build a fallback. A scheduled Apex job or Flow that polls for envelopes stuck in “sent” status for more than 24 hours catches the rare webhook that never arrives, whether from a network blip or a provider outage.
What Security and Compliance Checks Matter Before Go-Live?
Every signed document needs a tamper-evident audit trail: who signed, when, from what IP address, and what document version they saw. Most eSignature platforms generate this automatically, but confirm it’s actually being captured and stored somewhere durable, not just displayed in a UI that disappears after 90 days.
For most commercial contracts, standard ESIGN and UETA compliance is sufficient, since these federal and state frameworks already establish that electronic signatures carry the same legal weight as ink. Healthcare workflows are different. If your signature workflow touches protected health information, anywhere in the document or the signer’s identity data, you’re operating under HIPAA, which requires additional controls around encryption, access logging, and business associate agreements with your eSignature vendor.
Storage architecture is a real decision, not a default setting:
- Attaching signed PDFs directly to the Salesforce record keeps everything in one place and is simplest for smaller orgs.
- External or bring-your-own-cloud (BYOC) storage gives you control over data residency and retention policy, which matters for regulated industries or organizations with strict internal data governance.
- Treat the signed document and its audit metadata as a first-class record. Building a transaction object that stores envelope metadata and links to the Files object lets you run status dashboards and apply retention policy the same way you would for any other Salesforce data.
Whatever you choose, lock down field-level security on signature status and document fields, and pair your eSignature workflow with a compliance checklist covering authentication, retention, and encryption at rest.
How Do You Test and Troubleshoot the Integration?
Run through this sandbox test plan before promoting anything to production:
- Send a test envelope from a record page and confirm it reaches the recipient with the correct template and pre-filled fields.
- Sign it yourself using a test account, ideally with multiple signers if your workflow requires sequential signing.
- Verify write-back by checking that signature date, status, and any collected fields land correctly on the Salesforce record.
- Retrieve the signed PDF and confirm it attaches to the record’s Files or related list as expected.
- Trigger a decline and confirm your Flow or Apex logic handles that path correctly, not just the happy path.
When something breaks, check the connector’s own delivery logs first, since most vendors expose webhook delivery status and error codes in their admin console. In Salesforce, check debug logs on your Flow or Apex listener for parsing errors. The three most common failures are status fields that never update (usually a webhook or permission issue), missing PDFs (often a storage configuration or timing issue), and permission denied errors (almost always the integration user’s permission set missing object or field access).
For production monitoring, set up an alert on envelopes stuck in a pending state for more than a defined window, so a silent webhook failure doesn’t sit undetected for days.
Pro Tip: Keep a dedicated test template with dummy fields separate from your real business templates. It lets you validate connector health anytime without cluttering production data with test contracts.
How Does BeeSign Fit Into a Salesforce eSignature Rollout?
BeeSign gives Salesforce admins the pieces this entire workflow depends on: reusable templates, a developer REST API for building custom automation, identity verification with government ID capture and biometric face matching for higher-assurance signing, and complete audit trails that satisfy the compliance checks covered above.
For organizations with data residency requirements or strict branding needs, BeeSign’s white-label and bring-your-own-cloud storage options mean your signing experience runs under your own domain, and signed documents stay inside infrastructure you control rather than a vendor’s shared cloud.
A sandbox pilot looks like this: install the connector, build two or three real templates instead of generic placeholders, configure your webhook or Flow-based status sync, and validate write-back to the actual objects your team uses daily. This is the same pattern used in a 30 day HubSpot integration pilot, and it applies just as well inside Salesforce. For a concrete look at how embedded signing fits into an existing system’s workflow, review this embedded integration example.
What Should Admins Actually Prioritize?
Most teams overthink the embedded versus API-first decision. If your reps live inside standard Opportunity or Contract page layouts, embedded signing wins on speed to value. Save the API-first approach for orgs that need custom document assembly or cross-system orchestration, since that flexibility comes with real setup overhead you shouldn’t take on unless you need it.
A realistic timeline for a small-to-medium rollout is two to four weeks: one week for prerequisites and sandbox setup, one to two weeks for template mapping and webhook configuration, and a final week for testing and staged production rollout. Budget for one admin at roughly half capacity, not a full engineering team, unless your document logic is genuinely complex.
The mistake I see most often isn’t a bad vendor choice. It’s skipping the sandbox testing phase because a demo looked clean. Demos never show you a stuck webhook at 4 p.m. on a Friday.
— Mustafa Abusharkh
Ready to Pilot eSignature Inside Your Salesforce Org?
The platform offers predictable, flat-rate pricing without per-envelope fees, which can be beneficial as signature volume grows. Combined with white-label branding, bring-your-own-cloud storage, and a REST API built for exactly the webhook and Flow automation covered above, it’s designed for admins who want the integration built once and left alone, not re-negotiated every renewal.
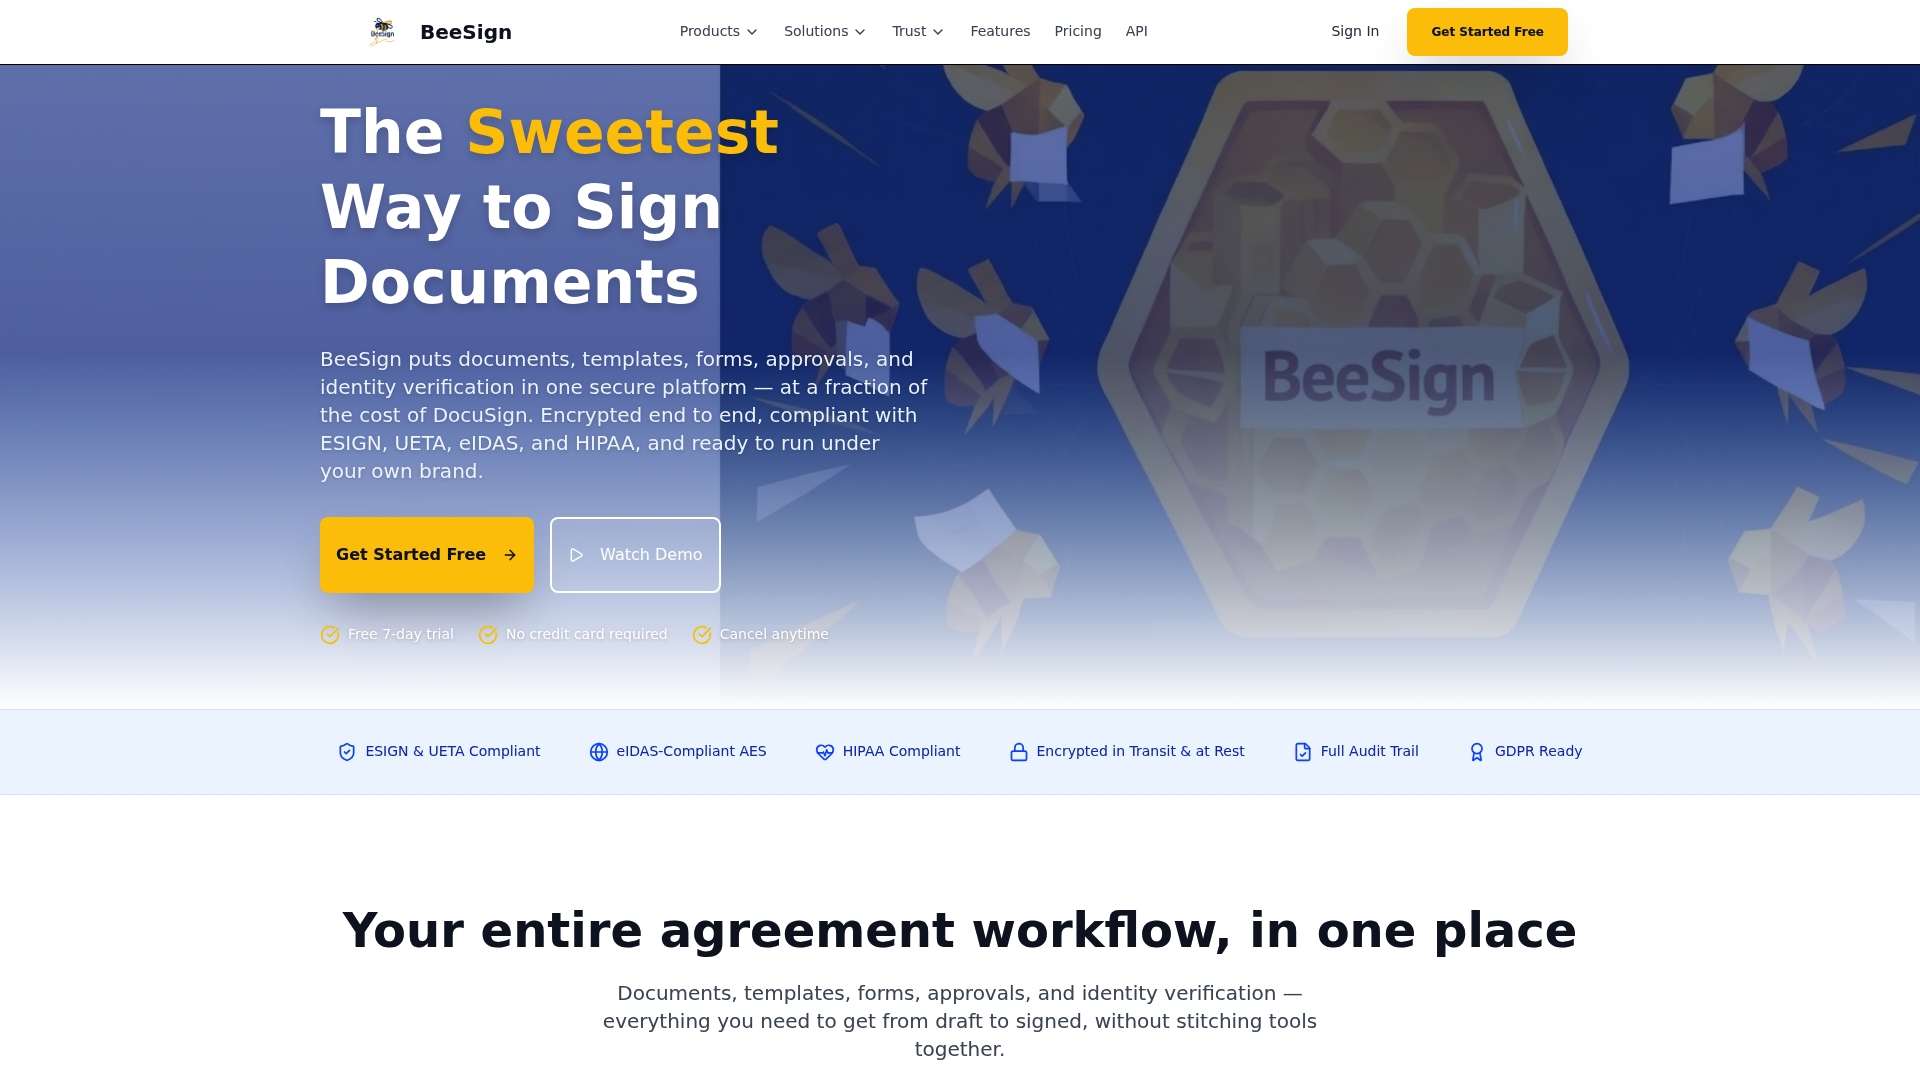
Start with the Electronic Signatures product page to see how templates, identity verification, and audit trails work together, then check the pricing page to compare the Individual plan at $9.99 per month against the Enterprise tier for larger teams. If your org needs custom-built integrations rather than a self-managed connector, BeeSign’s customized integrations service builds and maintains the connection for you.
For your pilot, keep it small: install in a sandbox, run three real test templates through a full send-and-sign cycle, and confirm your webhook or Flow sync updates records correctly before you schedule a production rollout. That’s the whole checklist. Start your sandbox trial today and see how it fits your workflow within a week.
Sources
- Hhs
- Complete guide to Salesforce eSignature solutions | SalesforceBen
- E-signature Software | G2
- DocuSign and Salesforce integration with webhooks | Omnitoria
FAQ
Can Salesforce Integrate With DocuSign?
Yes, Salesforce integrates with DocuSign and similar eSignature platforms, typically through a managed package that adds Send and Sign buttons to record pages and syncs status back through webhooks or outbound messages. The same integration pattern, install a connector, authorize the account, map fields, configure sync, applies across most major eSignature providers, including BeeSign.
Can I Create a Digital Signature in Salesforce?
Salesforce itself doesn’t include native eSignature capture, so you need a connected third-party tool or API integration to collect legally binding signatures. Once connected, signature requests, template selection, and status tracking all happen directly from the Salesforce record page.
How Do I Set Up an Email Signature in Salesforce?
An email signature (the text block at the bottom of outgoing emails) is unrelated to eSignature integration and is configured under your personal Salesforce settings or through email templates, not through a signing connector. If you’re looking to set up document signing rather than email formatting, that requires installing an eSignature connector like the ones covered throughout this guide.
What Is DocuSign Integration?
DocuSign integration refers to connecting the DocuSign platform to another system, in this case Salesforce, so signature requests, document templates, and status updates flow directly between the two without manual data entry. The integration typically uses OAuth authorization, a managed package, and webhook-based status sync to keep records current.
How Much Does BeeSign Cost for a Salesforce Integration?
BeeSign offers a subscription plan starting at a monthly fee, with Enterprise pricing available on request through the pricing page. Customized integration builds are also priced individually based on scope.
Recommended
Ready to transform your workflow?
Start using BeeSign today and experience the future of document signing