Admins: Set Signer Roles and Permissions Right in 7 Steps
Platform-agnostic admin resource with a 7-step checklist to map signer roles to template placeholders, assign verification tiers, and stop template rebuilds.
Signer roles and permissions define who must act on a document and exactly what each participant can do with it. The single best move for any admin: map every required action, sign, approve, view, prep, to a discrete role before you touch a template. Standards like ESIGN and HIPAA don’t dictate your role structure, but they do demand the audit trail and access controls that a clean role setup, the kind that makes this possible.
TL;DR:
- Assign roles based on the specific function each participant performs, not their job titles, to prevent errors and ensure templates remain reusable.
- Use placeholders like signer_1 or approver in templates for recurring documents and assign individual identities only for one-off or legally mandated signatures.
- Implement strict identity verification levels matched to document sensitivity, from email verification for internal use to biometric matching for high-value or regulated agreements.
- Choose sequential signing when data dependencies or witness requirements exist, otherwise opt for parallel signing to reduce completion times for independent signers.
- Maintain a lean role structure, typically five roles or fewer, and regularly review role assignments, audit trails, and access controls to stay compliant and prevent operational mistakes.
Table of Contents
- Understanding Signer Roles and Permissions in Signing Workflows
- What Each Signer Role Can and Can’t Do
- Sequential vs. Parallel Signing: Which Order Fits Your Workflow
- How Templates Turn Roles Into Reusable Fields
- Admin Controls: Setting Up Role-Based Access and Auditing Signer Activity
- Identity Verification Levels That Should Shape Signer Permissions
- A Step-by-Step Checklist for Assigning Signer Roles
- Why Most Teams Overbuild Their Role Structure
- Put This Role Structure to Work With Beesign
- Sources
- FAQ
Understanding Signer Roles and Permissions in Signing Workflows
Roles exist because a document without defined participant boundaries is a liability; for useful background on collaborative editing and invitation workflows, see can i invite someone to edit with me? — Feature requests — Alhora. Every recipient touching an agreement needs a scope, otherwise you get accidental edits, skipped signatures, or a viewer who somehow gains the ability to reassign the whole envelope. An agreement requires at least one participant who actually signs it, and Zigned’s documentation on participant roles frames this as the baseline: roles determine who must act and what actions they’re allowed to take. Everything else, approvals, notifications, prep work, builds around that core requirement.
Three things drive the need for structured roles:
- Restricting actions. A role limits what a participant can do, so a viewer can’t sign and a signer can’t cancel the envelope.
- Capturing consent cleanly. Separating “signed” from “approved” from “was notified” keeps your legal record unambiguous.
- Enabling audit trails. Every role assignment creates a traceable link between a person and an action, which is what regulators and courts actually check.
Most e-signature platforms group recipients into five broad categories, and Documenso’s recipient roles documentation lists a version of this same set: signer, approver, sender or issuer, CC or viewer, and assistant or preparer. A signer completes required fields and applies a signature. An approver reviews and either clears or rejects the document, sometimes without signing it themselves. The sender or issuer owns the envelope, meaning they can edit, reassign, or cancel it. A CC or viewer role exists purely for visibility, no field access, no action rights. An assistant or preparer fills in information on behalf of someone else, often before that person ever sees the document.
Here’s a decision point that trips up a lot of teams: should you assign a role to a placeholder (“Signer 1”) or to a specific named person at template creation? Use placeholders when the same document type goes out repeatedly with different people in the same functional slot, a lease, an offer letter, a vendor NDA. Assign specific individuals only when the workflow is one-off or when the legal requirement ties the signature to a named party from the start, like a notarized affidavit. Getting this distinction wrong is the single most common reason admins end up rebuilding templates from scratch six months in.
What Each Signer Role Can and Can’t Do
Permissions are where role theory turns into daily operational reality. Here’s what each common role actually controls once a document goes out for signature.
- Signer: Must complete every field marked required, apply a legally binding signature, and can typically download a copy once the envelope completes. A signer cannot edit fields assigned to another recipient, add new fields, or reassign the document to someone else.
- Approver: Reviews content and either approves or rejects it. Depending on the platform, an approver may also need to sign; some workflows treat approval and signing as separate steps entirely, which matters for contracts that need a supervisor’s sign-off before a signature is even collected.
- Sender or issuer: Holds the broadest rights on the sending side, reassigning recipients, canceling or voiding an envelope mid-flight, and managing which templates are available to use. This role should map to a small, trusted group, not every team member who happens to send documents.
- CC or viewer: Gets notified and can see the document, but has no field access and no action rights. Treat this role as read-only by design, not by convention.
- Assistant, preparer, or witness: Prefills data for someone else or observes a signature event without necessarily signing. According to Documenso’s role documentation, assistant roles often require sequential signing specifically, because they prefill fields that later recipients depend on. Enable that role in a parallel flow and the prefill assumption breaks down, fields show up empty for the next signer.
Edge cases deserve a second look before you launch a workflow into production. Sign-on-behalf and delegated signing (someone signing under another person’s authority, common in corporate and power-of-attorney contexts) need explicit configuration and, in most jurisdictions, a documented authorization on file. Legal witness requirements vary by document type and by state, so don’t assume your platform’s “witness” role satisfies a statutory requirement without checking the underlying law first.
Pro Tip: Before assigning a role, write down the single sentence that describes what happens if that role is compromised, an approver who shouldn’t sign, a viewer who somehow edits. If you can’t write that sentence, the role scope is too loose.
Sequential vs. Parallel Signing: Which Order Fits Your Workflow
Signing order changes what a role can physically do at the moment it’s their turn. Sequential signing sends the document to one recipient at a time, in a defined order, which is required whenever an assistant or preparer needs to fill fields before the next person sees them, and often required for witness-dependent signatures too. Parallel signing sends the document to every signer simultaneously, cutting completion time dramatically for documents where order doesn’t matter legally.
Pick your model with this checklist:
- Does any recipient need to see data another recipient enters first? If yes, use sequential.
- Is a witness or notary involved? Sequential, almost without exception.
- Are all signers independent, no dependency on prior input? Parallel gets you faster completion, often within hours instead of days.
- Does the agreement need staged approval before signing? Build conditional routing: approver first, then signer, then a final countersign from the issuer.
- Are you optimizing for speed over strict control? Default to parallel unless a specific role forces sequential behavior.
Multi-stage approval is where these two models blend. A common pattern: legal reviews and approves, then the counterparty signs, then an internal executive countersigns, three stages, each potentially sequential internally, with parallel signing used only within a stage where multiple equal-standing signers exist.
How Templates Turn Roles Into Reusable Fields
A template only stays useful if its fields stick to the right person every time it’s sent, and that’s a role mapping problem, not a formatting one. Instead of hardcoding an email address to a signature field, platforms let you assign fields to a role placeholder, something like signer_1 or approver, so the template itself never changes. Only the person filling that role changes at send time. Formalingo’s documentation on signer roles describes exactly this pattern: role identifiers keep a template reusable across different recipients without any redesign.
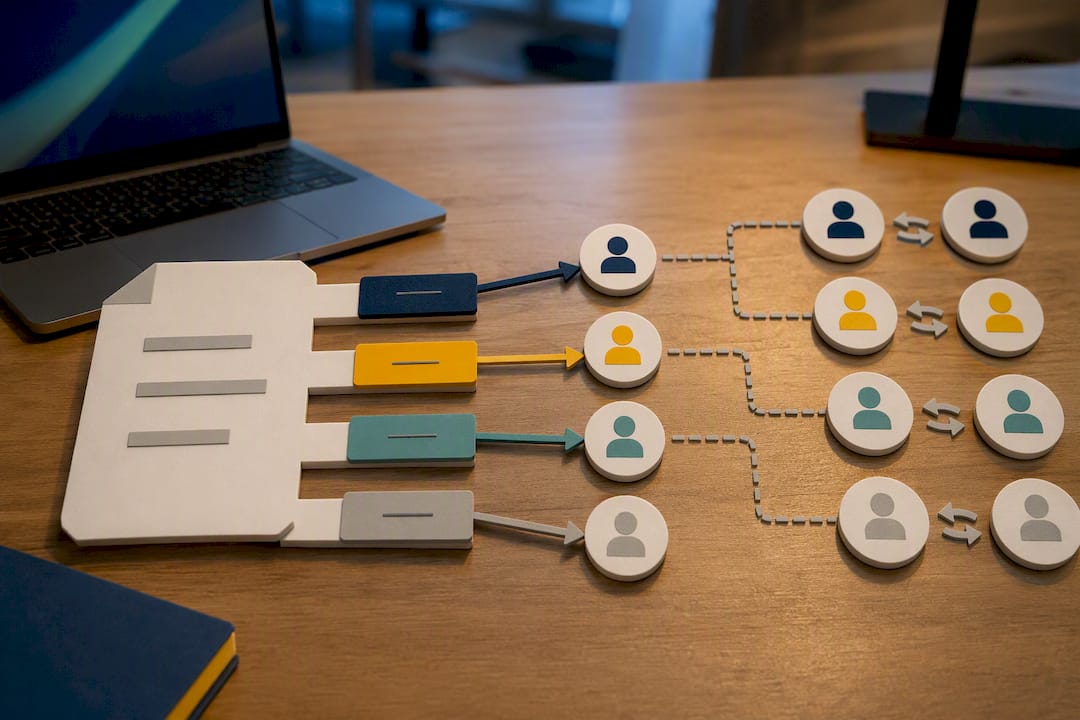
This matters practically because manual reassignment is where errors creep in. A field that was correctly mapped to “Signer 1” for your first ten sends stays correctly mapped for send eleven, because the role, not the person, owns the field. Skip this and you’re rebuilding field placement every single time someone new needs to sign, which is both slow and a common source of misplaced signature blocks.
A few habits keep a template library from turning into a mess:
- Name roles by function, not by department or individual (
approver, notsarah_from_legal). - Keep a single naming convention across your entire template library,
signer_1,signer_2, not a mix of numbering styles. - Retire templates that no longer match your current role structure instead of patching them indefinitely.
On the developer side, most REST APIs expose roles as structured objects on the template payload, letting an integration assign a real recipient to a role identifier programmatically at send time, which is how automated onboarding or contract-generation pipelines populate signer fields without a human touching the template.
Admin Controls: Setting Up Role-Based Access and Auditing Signer Activity
Recipient roles control what a signer can do inside one document. Role-based access control, RBAC, controls what your team members can do across the whole platform, who can create templates, who can send on the organization’s behalf, who can void a live envelope. You need both layers, and conflating them is a common admin mistake.
Microsoft’s Azure Artifact Signing documentation illustrates the pattern well outside the e-signature world: RBAC definitions grant precise actions, managing identity validation requests, signing with a specific certificate profile, rather than blanket access. Apply that same precision internally. Typical admin capabilities worth scoping separately include assigning which templates a team can use, managing role assignments on active envelopes, revoking or canceling documents, and setting identity-verification requirements per document type.
- Grant template creation rights only to people who actually build workflows.
- Reserve cancel/void rights for a small administrative group.
- Require identity verification settings to be locked at the template level, not left to individual senders.
- Review role assignments quarterly, or immediately after any team change.
AWS Signer’s permission model demonstrates a related concept worth borrowing: cross-account signing grants profile-specific permissions so one account can authorize another to sign without handing over full control, a useful pattern if your organization shares signing infrastructure across departments or subsidiaries.
Pro Tip: Separation of duties isn’t just a compliance checkbox. The person who can create a template shouldn’t automatically be the person who can also cancel a live envelope, those are two different failure modes, and combining them in one login is how a single mistaken click voids a contract that already has three signatures on it.
Your audit trail is the record that proves all of this worked as intended. At minimum, retain who was assigned which role, when each action happened, and what identity verification, if any, backed each signature.
Identity Verification Levels That Should Shape Signer Permissions
How confident you are in a signer’s identity should directly determine how much authority that role gets. Email-link access alone is fine for a low-stakes internal form. It’s not fine for a document releasing sensitive financial or health data, and treating every signature request with the same verification bar is where a lot of compliance exposure hides.
Common verification tiers, in ascending strength:
- Email verification: confirms access to an inbox, nothing more.
- SMS one-time passcode: adds a second channel, reasonable for most business contracts.
- Knowledge-based authentication (KBA): questions drawn from public or credit records, used for higher-stakes consumer agreements.
- Government-ID capture: photographs or scans a legal ID against the signer’s claimed identity.
- Biometric or face match: compares a live selfie against the ID photo, the strongest common tier available today.
Stronger verification unlocks more permissive workflows. Remote notarization, release of protected health information, and high-value financial agreements generally warrant ID capture or biometric matching, not a bare email link. This is where Beesign’s own identity verification and security documentation are directly relevant: the platform’s security page details encryption in transit and at rest alongside audit trail features built to support defensible signer identity records.
A signature only carries the legal weight of the identity behind it. If you can’t produce the consent record, the ID capture, and the audit trail on demand, the signature itself is doing less work than you think it is.
Hold onto consent language, ID captures, and the full audit trail for every document where ESIGN or HIPAA defensibility matters, not just the ones that feel risky at the time. Beesign’s guide on verifying signer identity online walks through choosing a verification tier that matches the document’s actual stakes.
A Step-by-Step Checklist for Assigning Signer Roles
Work through these steps in order every time you build a new workflow, and skip none of them, even for a document that feels routine.
- Plan roles first. List every participant type before you open the template builder, signer, approver, viewer, assistant.
- Create or select the template. Start from an existing template if the role structure already matches.
- Map fields to role placeholders. Assign each field to a role identifier, not a named individual, unless the send is genuinely one-off.
- Set signing order. Choose sequential if any role depends on another’s input; choose parallel otherwise.
- Add identity verification. Match the tier to the sensitivity of the document, per the levels above.
- Test with test accounts. Send the workflow to internal test addresses before it ever reaches a real recipient.
- Monitor logs after launch. Confirm the audit trail is capturing every action as expected.
In your test send, confirm three things specifically: that each field landed on the correct role, that notifications fired for the right recipients only, and that identity prompts appeared exactly where you configured them. Beesign’s approval workflow guide walks through a similar validation pass for multi-stage approval chains.
Pro Tip: The most common failure isn’t a broken integration, it’s a field left unassigned to any role. Unassigned fields default unpredictably depending on the platform, sometimes to the sender, sometimes to nobody. Check every field before you save a template as final.
If a recipient reports receiving the wrong fields, the fix is almost always a role mismatch in the template, not a platform bug. Re-open the template, confirm each field’s role assignment, and resend a test before troubleshooting anything further downstream.
Why Most Teams Overbuild Their Role Structure
Most teams default to more roles than they need, a separate role for every job title instead of every function. That’s backwards. A five-role structure, signer, approver, sender, viewer, assistant, covers nearly every real-world document workflow, and adding more roles than that usually just adds more places for a mapping error to hide. For a regulated team, HR, healthcare, finance, the fix isn’t more roles, it’s stricter identity verification and audit review on the roles you already have. Small teams can often run on three: signer, approver, and issuer. Whatever the size, review role assignments on a set schedule and document the role structure itself, not just who’s currently in each seat, so training a new admin doesn’t require rebuilding institutional memory from scratch.
— Mustafa Abusharkh
Put This Role Structure to Work With Beesign
Everything covered here, role placeholders on templates, tiered identity verification, audit trails, RBAC for your admin team, is handled by the platform without stitching together separate tools for each piece. Templates map fields to role identifiers so your library stays reusable, identity verification runs from email confirmation up through government-ID and biometric face matching, and every action lands in a compliance-ready audit trail.
If data residency or branding matters to your organization, Beesign’s white-label and BYOC options let you run the platform under your own domain with cloud storage that stays inside your own infrastructure, a meaningful difference from platforms that require your documents to live on their servers by default. The full feature set, templates, audit trail, identity verification, is outlined on the Beesign features page, and the Individual plan starts at $9.99 per month if you’re ready to configure your first role-based workflow. Enterprise teams needing custom integrations can review pricing and plan options directly, or start a free trial to test role mapping on a real template before committing.
Sources
- Assign roles in Azure Artifact Signing (tutorial) | Microsoft Learn
- Using cross-account signing with signing profiles | AWS Signer Developer Guide
FAQ
What Is the Difference Between a Signer and an Approver?
A signer must complete required fields and apply a legally binding signature, while an approver reviews content and either clears or rejects it, sometimes without signing at all. Some workflows require both roles in sequence: an approver signs off internally before the document ever reaches the actual signer.
Can Anyone Be a Signatory on a Document?
Anyone with the legal capacity to enter a binding agreement can generally act as a signatory, but the identity verification tier assigned to that role should match how sensitive the document is. Higher-stakes agreements, healthcare records, financial releases, warrant government-ID capture or biometric verification rather than a bare email confirmation, which platforms like Beesign support through tiered identity verification.
What Is a Signer’s Role Title in a Workflow?
A signer’s role title is simply the functional label assigned to that participant, “Signer 1,” “Approver,” or “Witness,” rather than a job title from their employer. Templates use these role identifiers as placeholders so the same document structure works no matter who fills the role at send time, as Formalingo’s documentation describes.
How Do Multiple Signers Work on the Same Document?
Multiple signers can complete a document either sequentially, one after another in a defined order, or in parallel, where every signer receives the request simultaneously. Sequential order is required whenever one signer’s input depends on a prior recipient’s entry, such as an assistant prefilling fields, per Documenso’s role documentation, while parallel signing is faster for independent signers with no such dependency.
Recommended
Ready to transform your workflow?
Start using BeeSign today and experience the future of document signing